


The OWASP Top 10 - (2025) — AppSec & Architecture Masterclass
Category: Tutorials
- views: 221
- date: 14 October 2026
- posted by: AD-TEAM

The OWASP Top 10 - 2025 — AppSec & Architecture Masterclass
Last updated 12/2025
Duration: 6h 17m | .MP4 1920x1080 30fps(r) | AAC, 44100Hz, 2ch | 7.44 GB
Genre: eLearning | Language: English
What you'll learn
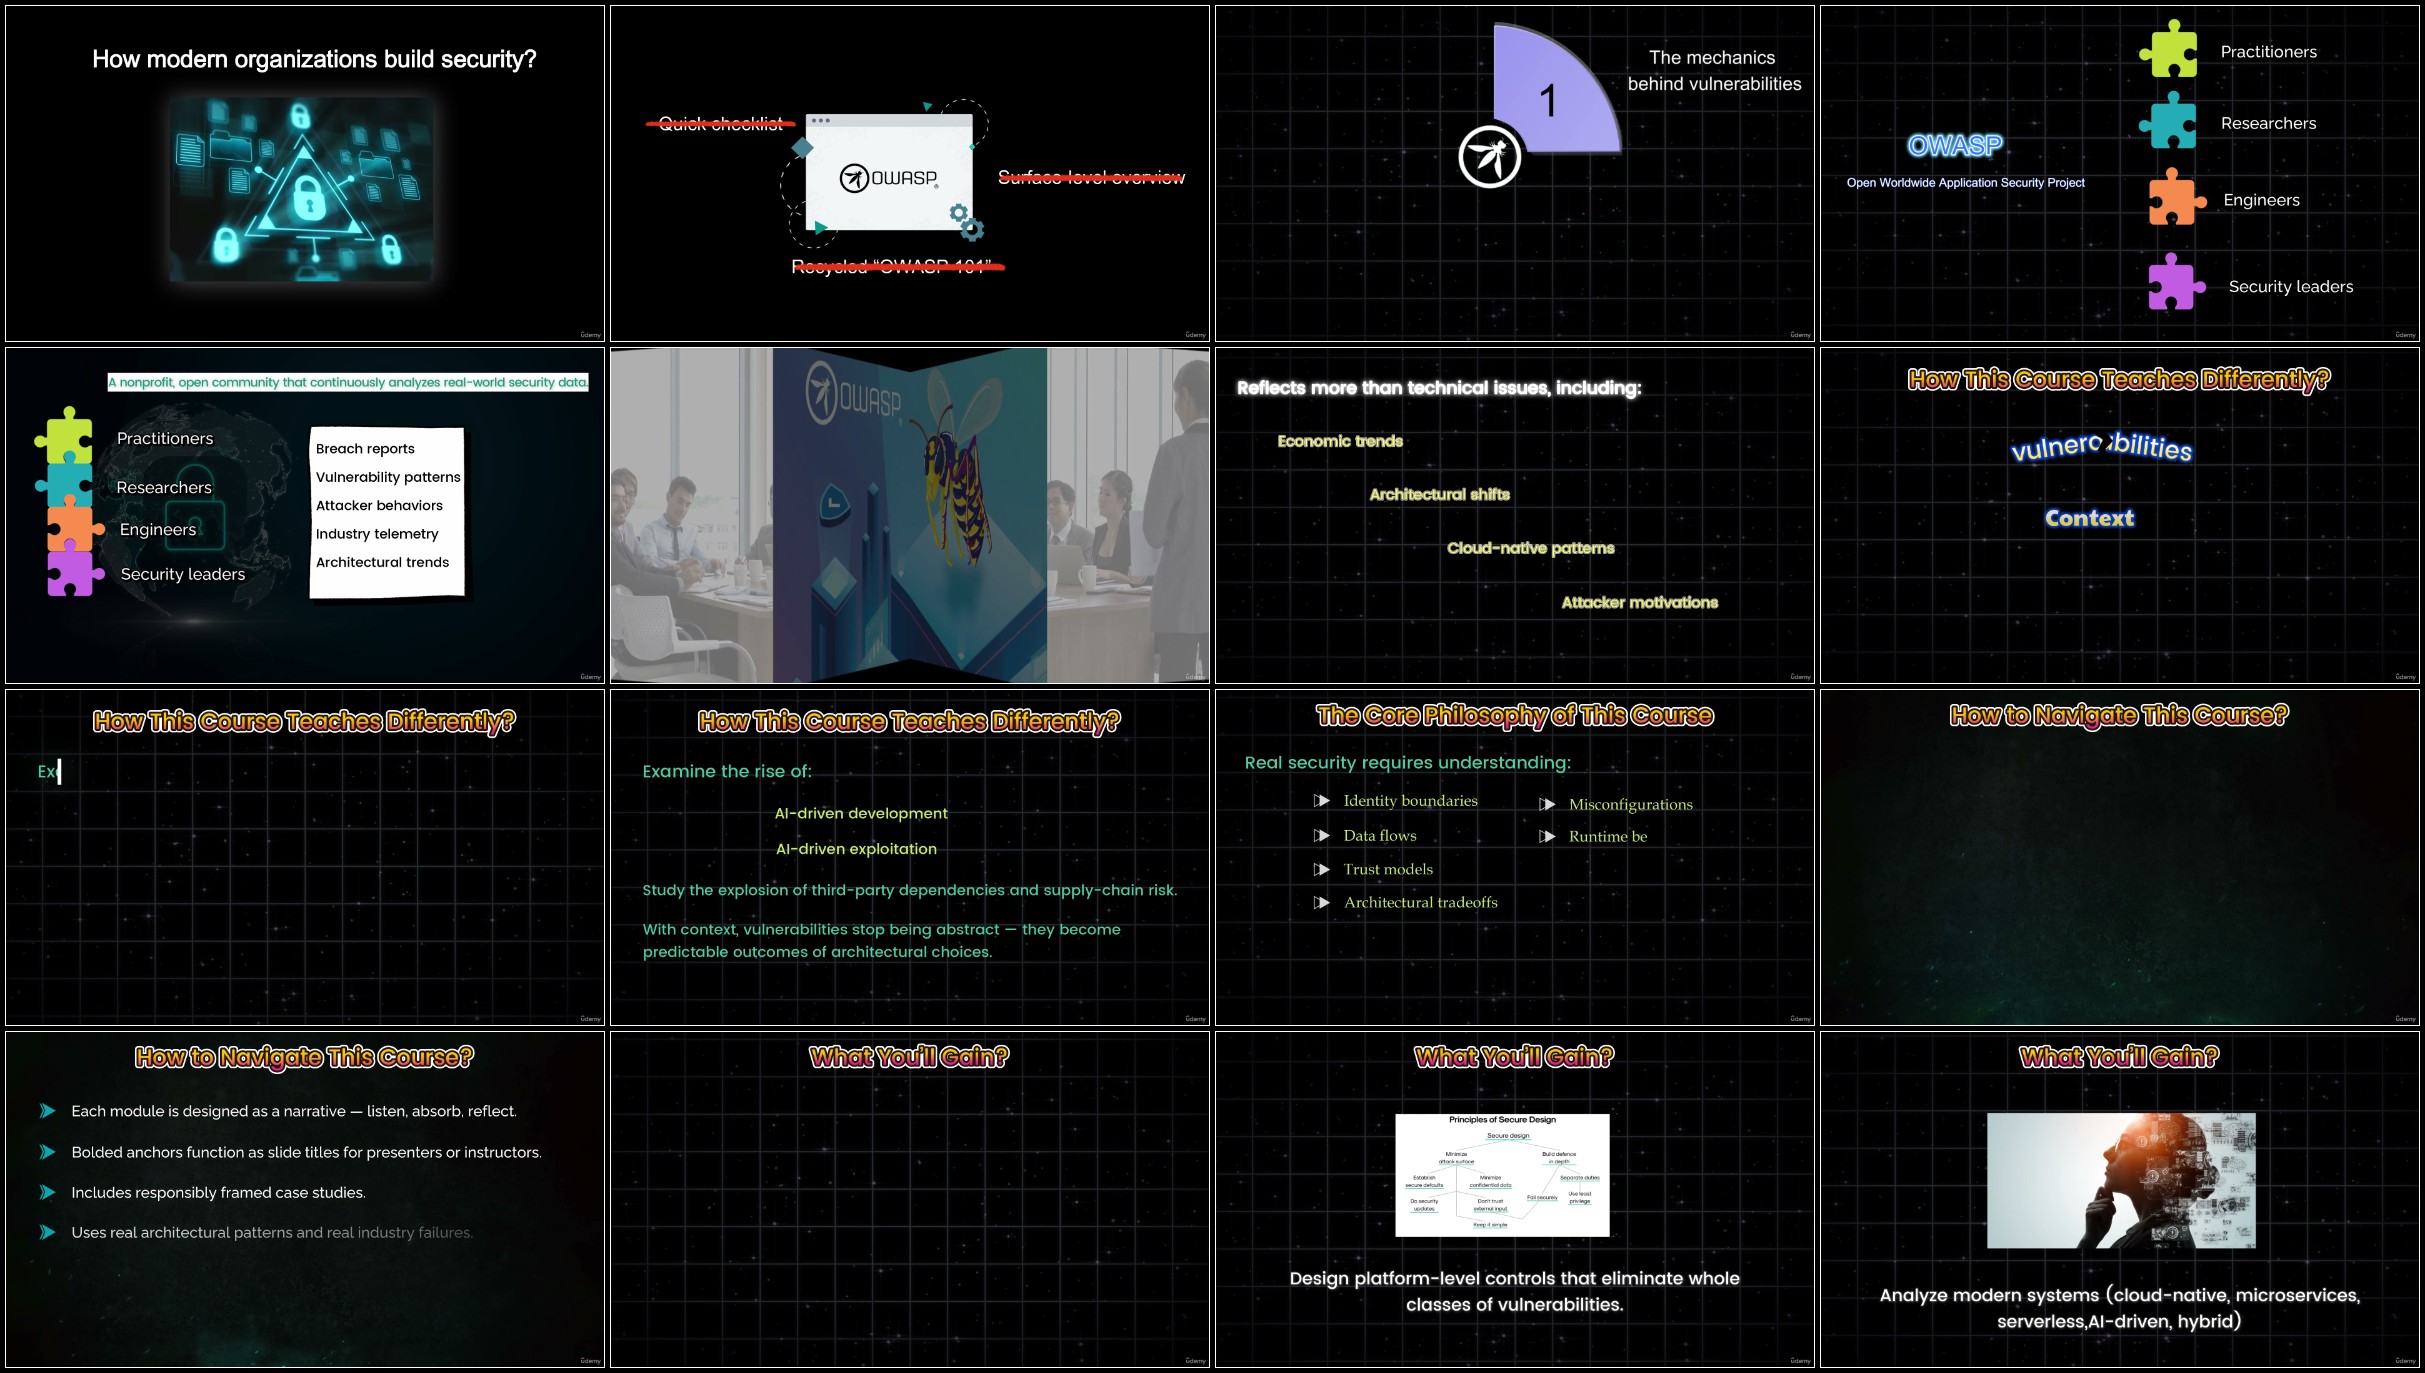
- Understand the real-world threat landscape from 2010–2025 and how it shaped modern AppSec.
- Explain each OWASP Top 10 category in architectural, business, and engineering terms — not just definitions.
- Map OWASP risks to modern architectures like cloud, APIs, microservices, and serverless systems.
- Think like an attacker and analyze how breaches unfold using realistic exploit chains.
- Build secure-by-design architectures with least privilege, defense-in-depth, and identity-first patterns.
- Apply OWASP ASVS, NIST 800-53, SOC2, and ISO27001 to enterprise security programs.
- Design platform-level controls that prevent entire vulnerability classes from being reintroduced.
- Create a sustainable AppSec roadmap for any company, using 30/90/365-day phases.
- Communicate risks to executives using professional security reporting frameworks.
- Lead AppSec efforts using Developer Security Champions, threat modeling, and security culture strategies.
Requirements
- Basic knowledge of web applications or API development
- Familiarity with cloud concepts (AWS, Azure, or GCP is helpful)
- Some exposure to DevOps, CI/CD, OR security tools
- No coding is required — but architectural thinking is essential
- Curiosity and willingness to think like both attacker and defender
- Beginners are welcome — but this course is designed to elevate mid-level or senior professionals to an AppSec & architecture leadership mindset.
Description
Modern applications don't fail because of bad code — they fail because of hidden architectural assumptions, broken trust boundaries, cloud misconfigurations, unreliable identity models, and software supply-chain complexity. The OWASP Top 10 isn't just a list of common vulnerabilities — it is a window into how modern systems actually break in the real world, and how attackers exploit the gaps that developers and architects don't always see.
This course goes far beyond definitions, checklists, or scanner outputs. It delivers a real-world, narrative-driven exploration of the OWASP Top 10 (2025 Edition) — not as isolated vulnerabilities, but asarchitectural failure patterns, business risk funnels, and attacker decision points. You will learn how these flaws emerge inside cloud-native applications, microservices, CI/CD pipelines, APIs, server less environments, event-driven systems, and AI-powered development workflows.
Every concept in this course is explained throughstorytelling, first-hand account style case studies, enterprise architecture breakdowns, and secure-by-design patternsthat you can immediately apply. You won't just understand how a breach happens — you'll understandwhy it happened,which assumptions failed,how attackers think, andwhich controls stop them without slowing product delivery.
You will see how identity flows through systems, how misconfiguration turns into privilege escalation, how supply-chain dependencies become lateral movement, how multi-tenancy fails quietly, and how a single unsecured request can become a full cloud-level compromise. You will also discover how real AppSec programs turn OWASP insights intoplatform guardrails,zero-trust architectures,runtime detection,signed artifacts,threat modeling workflows, andsecurity champion ecosystemsthat scale across large engineering teams.
This is not a theoretical course. This is a guided tour of how modern attacks unfold — and how properly designed architectures defeat them.
By the end, you won't see OWASP as a compliance checklist —You'll see it as amap of the modern attack surface.and ablueprint for building resilient systemsin 2025 and beyond.
Let us Begin!!
Who this course is for:
- Software Developers & Engineers
- Security Engineers & AppSec Specialists
- Solution & Enterprise Architects
- Platform Engineering Teams
- Security Leads / Managers / CISOs
- Technical Product Owners & Tech Leads
- Anyone preparing for AppSec or cloud security interviews
More Info
RapidGator
https://rapidgator.net/file/700a93469f473a61033575bbedc0ba76/
https://rapidgator.net/file/5f93dd4e3d46396a3afb43b901cdef05/
https://rapidgator.net/file/550fa192895ab0833c46e7d5be8dac83/
https://rapidgator.net/file/4847b90c41e03b0b502e38a45d9a19d0/
https://rapidgator.net/file/e823ef0a139e5579df14658edd2856bf/
https://rapidgator.net/file/466990619789e968b95790d1b0472996/
https://rapidgator.net/file/b4c21a45158bcfe1e0537f7ffd558337/
https://rapidgator.net/file/147aba137a3e8a81fb789f2dcf504183/
https://rapidgator.net/file/a9c5f4c70ca540ca65bdc3e1fbaf3c48/
DDownload
https://ddownload.com/slknr0g8sfvg
https://ddownload.com/n2thzhzh58m6
https://ddownload.com/i2phxn40rwgl
https://ddownload.com/3s28qrkdgbek
https://ddownload.com/uoch8taviazc
https://ddownload.com/j6acbi5y92zf
https://ddownload.com/pze6nsvw4qpq
https://ddownload.com/qpzkkfizzt3r
https://ddownload.com/zwdbc2gw4aye
NitroFlare
https://nitroflare.com/view/3808F0EDE84736D/
https://nitroflare.com/view/2200EC2B6171887/
https://nitroflare.com/view/57FC54FD9D4DF09/
https://nitroflare.com/view/D4E1E26032B8FC3/
https://nitroflare.com/view/3480A669E4C5FB1/
https://nitroflare.com/view/6511E64B9AC9AAB/
https://nitroflare.com/view/1507E80B60FE184/
https://nitroflare.com/view/656DBD2E6F24EB8/
https://nitroflare.com/view/1EC7EEBFA322F4F/
We need your support!
Make a donation to help us stay online

Bitcoin (BTC)
bc1q08g9d22cxkawsjlf8etuek2pc9n2a3hs4cdrld

Bitcoin Cash (BCH)
qqvwexzhvgauxq2apgc4j0ewvcak6hh6lsnzmvtkem

Ethereum (ETH)
0xb55513D2c91A6e3c497621644ec99e206CDaf239

Litecoin (LTC)
ltc1qt6g2trfv9tjs4qj68sqc4uf0ukvc9jpnsyt59u

USDT (ERC20)
0xb55513D2c91A6e3c497621644ec99e206CDaf239

USDT (TRC20)
TYdPNrz7v1P9riWBWZ317oBgJueheGjATm
Information |
|||
 |
Users of GUESTS are not allowed to comment this publication. | ||