


Operating System Forensics [Released: 9/16/2024]
Category: Tutorials
- views: 106
- date: 6 November 2024
- posted by: AD-TEAM

Operating System Forensics [Released: 9/16/2024]
.MP4, AVC, 1280x720, 30 fps | English, AAC, 2 Ch | 1h 41m | 218 MB
Instructor: Jungwoo Ryoo
Criminals rely on the intricacies of operating systems like Windows, macOS, and Linux to conceal their activities and hide data. However, a skilled digital forensics expert knows the places to look and the tools to use to access evidence of their crimes. This course covers all the major concepts and tools of the growing field of operating system forensics.
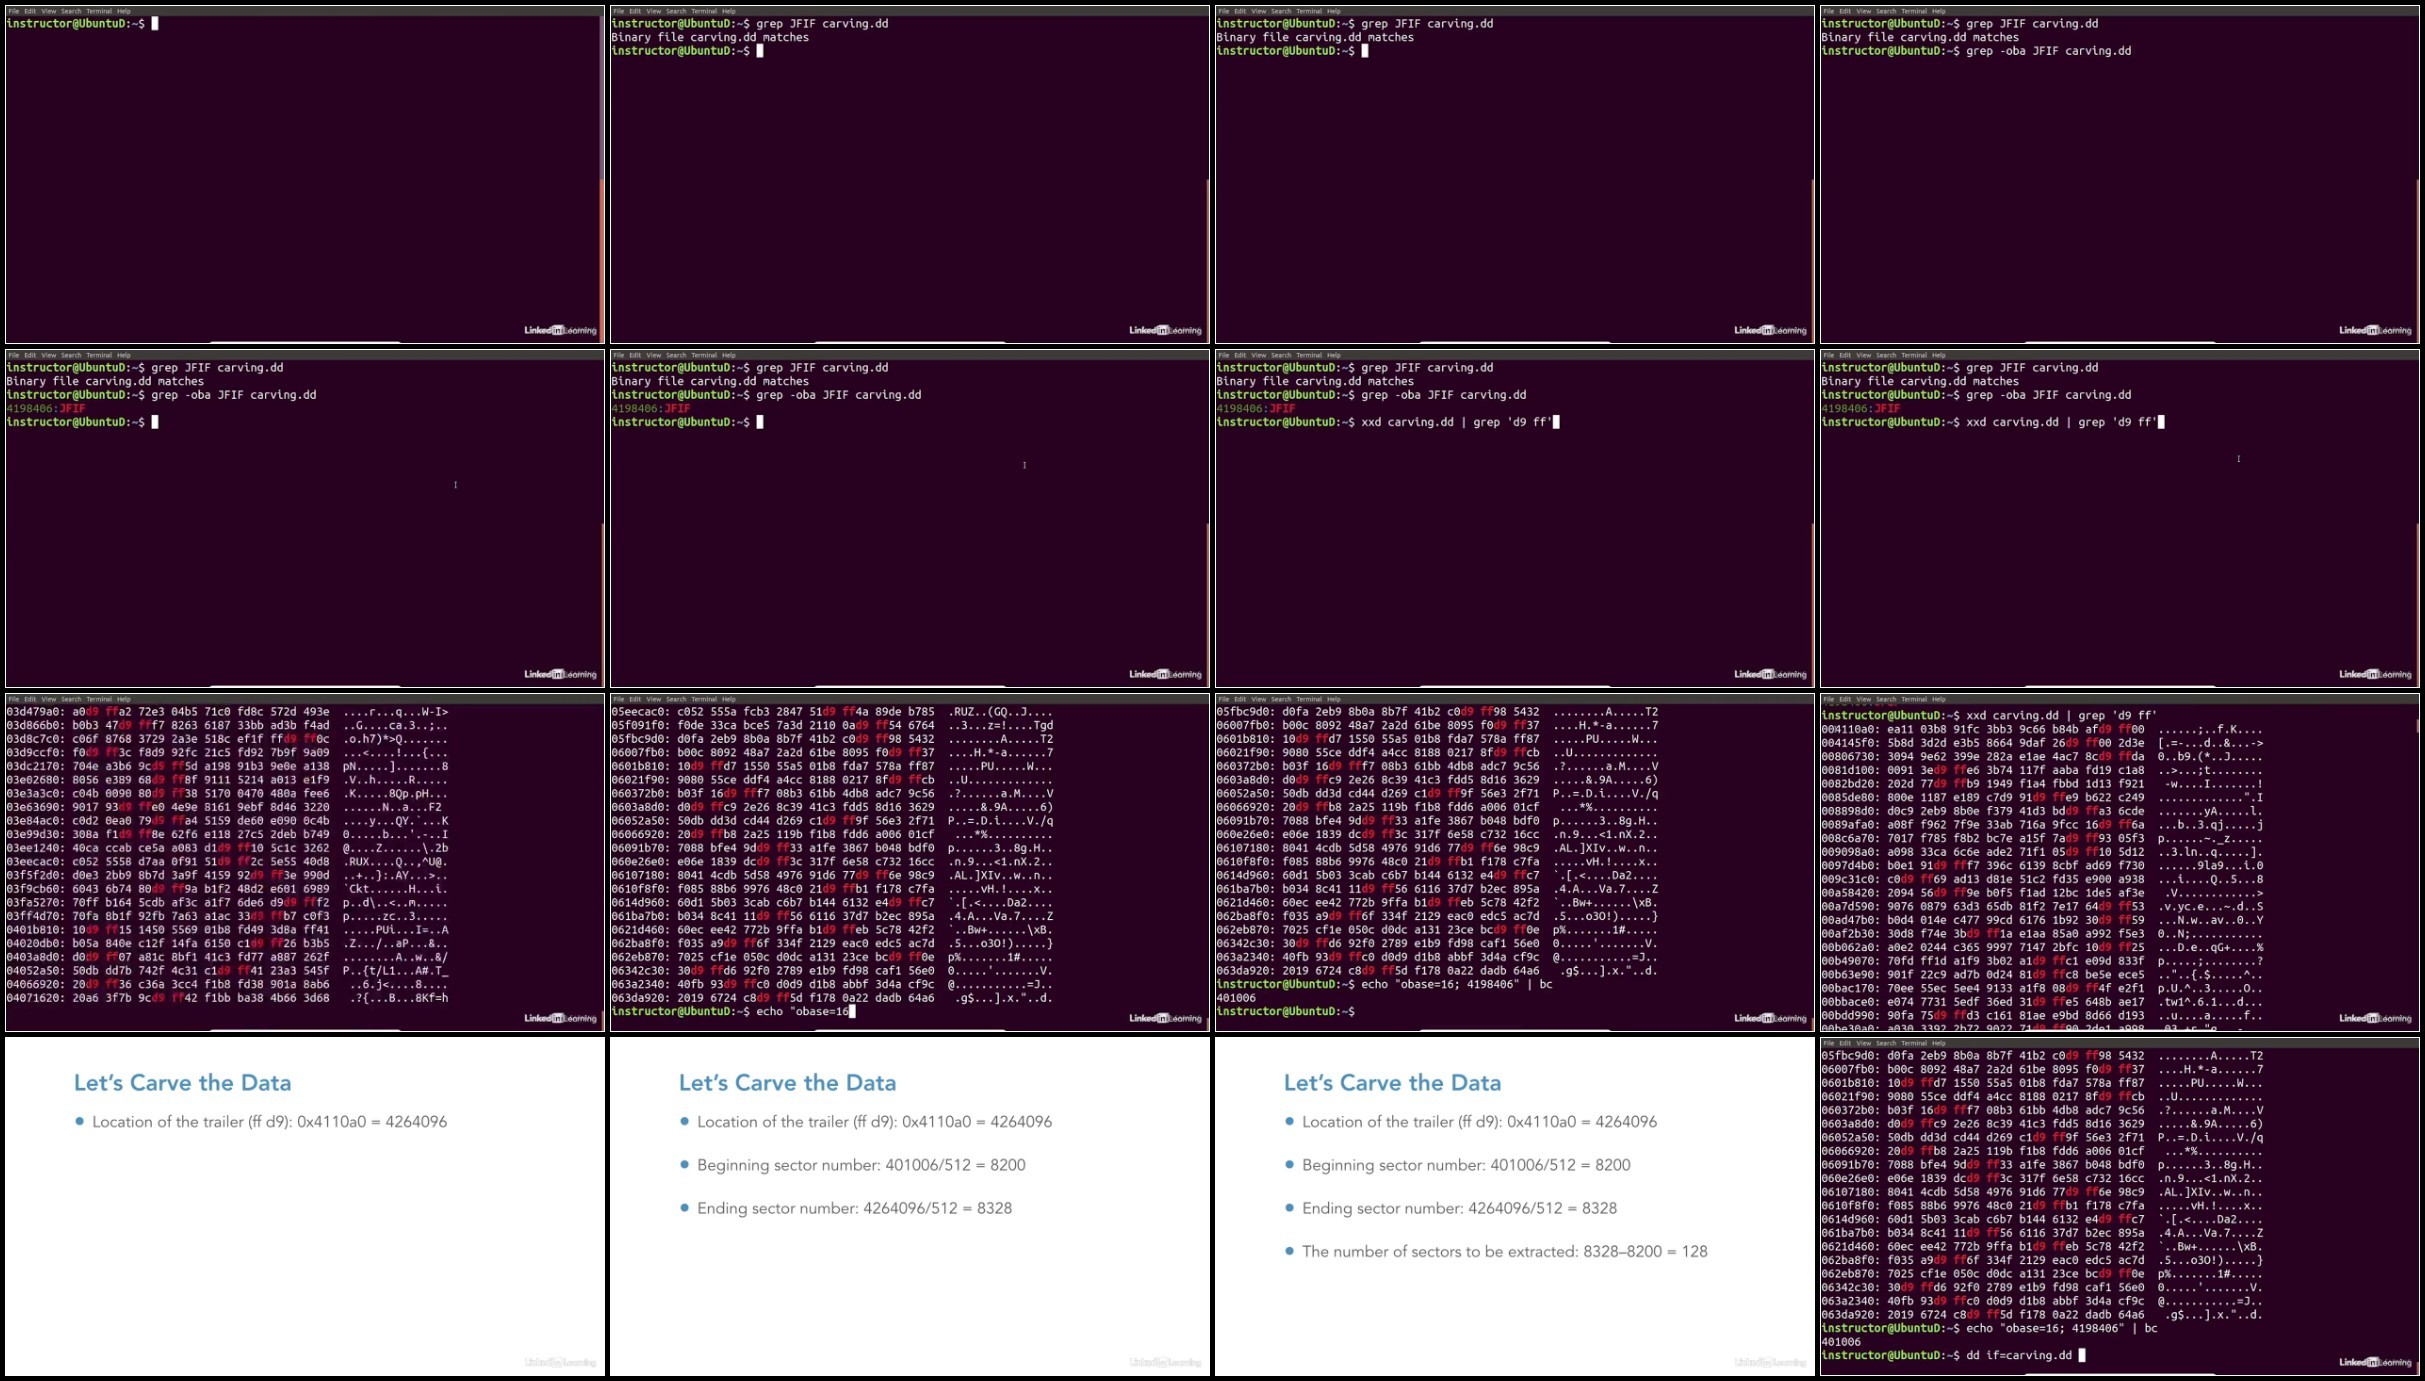
Instructor Jungwoo Ryoo (J.R.) reviews the fundamentals: the goals, history, and roles of operating system forensics and the future of the industry. He then shows how to acquire evidence from file systems, slack space, alternate data streams, and main memory. Jungwoo uses a combination of free and commercial software, so you can practice techniques like file recovery and live acquisition with the tools that are within your budget.
Learning objectives
- Understanding operating system forensics.
- Understanding job prospects in operating system forensics.
- Using GParted.
- Using Hex editors.
- Preparing for certifications.
- Acquiring data from various sources including file systems, main memory, and operating system logs.
More Info
Download
RapidGator
FileStore
DDownload
TurboBit
RapidGator
FileStore
DDownload
TurboBit
We need your support!
Make a donation to help us stay online

Bitcoin (BTC)
bc1q08g9d22cxkawsjlf8etuek2pc9n2a3hs4cdrld

Bitcoin Cash (BCH)
qqvwexzhvgauxq2apgc4j0ewvcak6hh6lsnzmvtkem

Ethereum (ETH)
0xb55513D2c91A6e3c497621644ec99e206CDaf239

Litecoin (LTC)
ltc1qt6g2trfv9tjs4qj68sqc4uf0ukvc9jpnsyt59u

USDT (ERC20)
0xb55513D2c91A6e3c497621644ec99e206CDaf239

USDT (TRC20)
TYdPNrz7v1P9riWBWZ317oBgJueheGjATm
Information |
|||
 |
Users of GUESTS are not allowed to comment this publication. | ||