


Reverse Engineering Frida for Beginners
Category: Tutorials
- views: 237
- date: 13 June 2024
- posted by: AD-TEAM
Reverse Engineering Frida for Beginners
Genre: eLearning | MP4 | Video: h264, 1280x720 | Audio: AAC, 44.1 KHz
Language: English | Size: 2.89 GB | Duration: 5h 14m
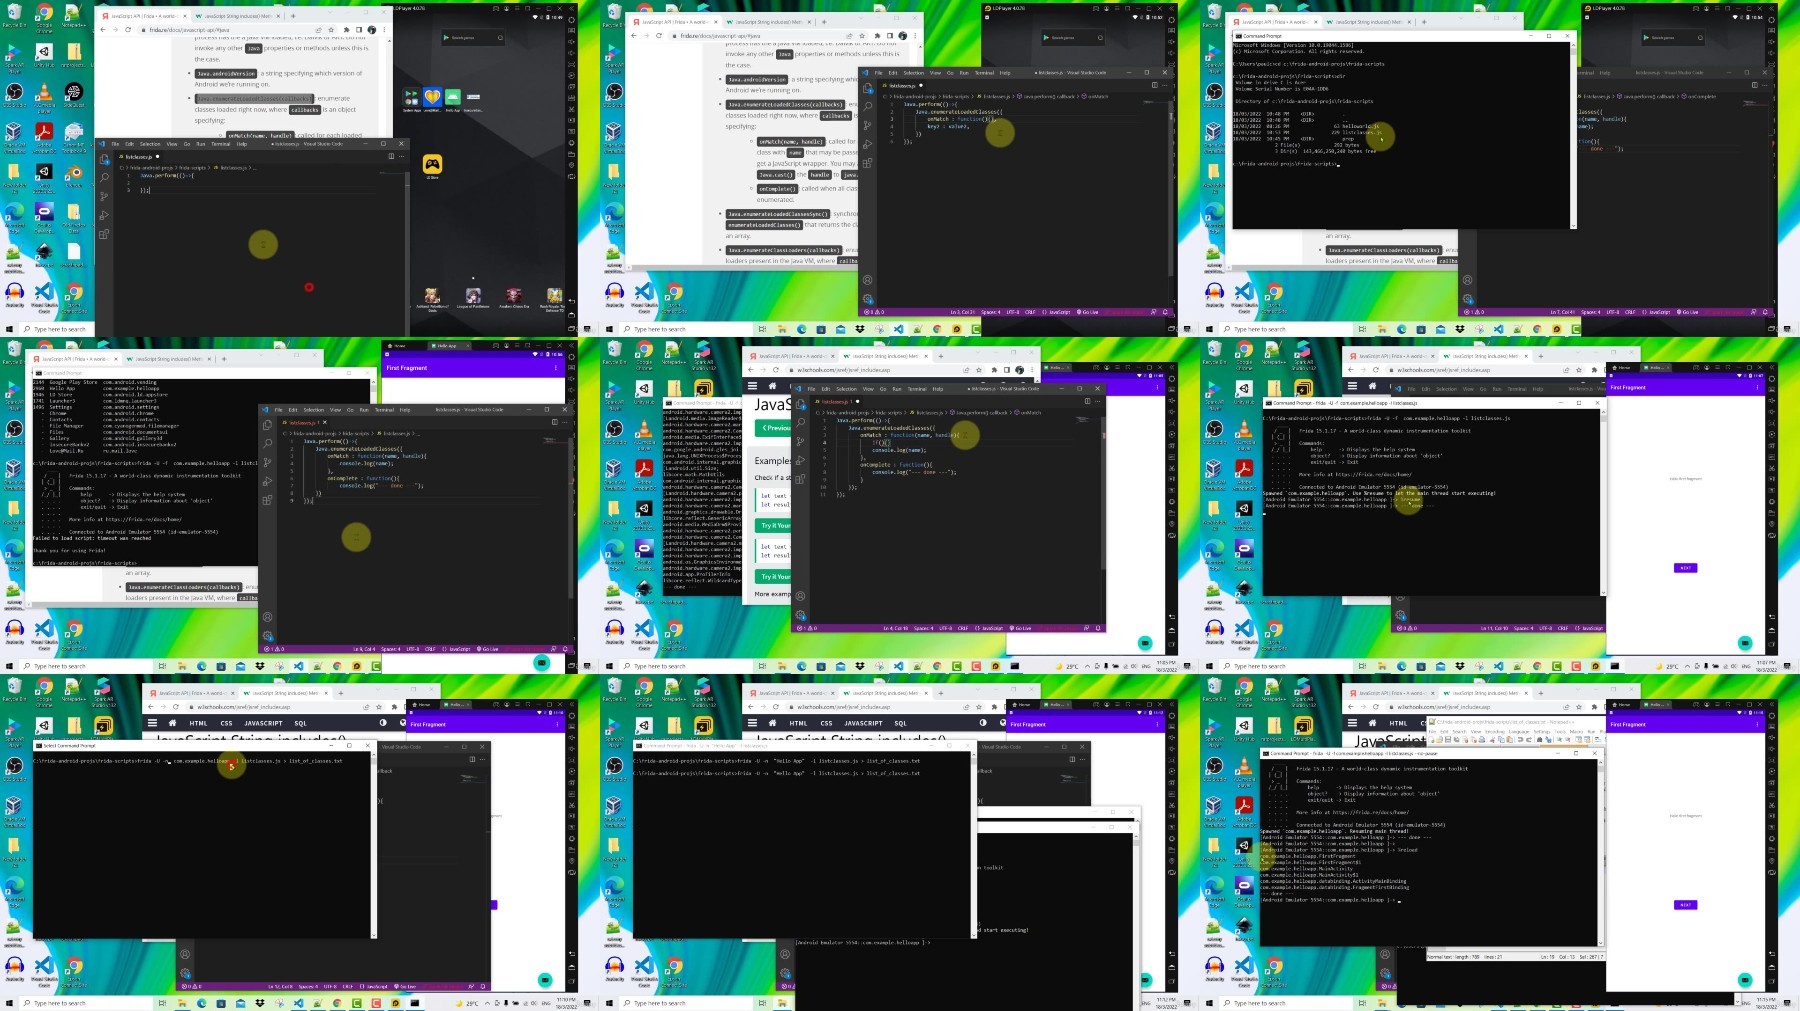
A beginner's introduction to reverse engineering Android and windows applications using the Frida toolkit
What you'll learn
Listing process libraries
Reversing Android apps
Hooking Classes and Functions
Examining and modifying function parameters and return values
Reversing windows app
Hooking process functions
Memory scanning
Process injection
Hacking memory
Decompiling apps
Bypassing root detection
Interceptinghttp andhttps traffic
Bypassing basic security mechanism for android and windows apps
Enumerating libraries and imported functions
and more..
Requirements
PC Laptop and non-rooted android phone (optional)
Basic Java/jаvascript would be helpful but not mandatory
Description
Frida is a dynamic instrumentation toolkit for developers, reverse-engineers, and security researchers. It allows you to inject your own scripts into black box processes. Hook any function, spy on crypto APIs or trace private application code, no source code needed. Edit, hit save, and instantly see the results. All without compilation steps or program restarts. It's the swiss army knife for process injections for native apps and is a popular dynamic code instrumentation toolkit. It lets you inject snippets of jаvascript or your own library into native apps on Windows and Android. It is the go-to tool you use for API tracing.
At the end of this course you will be able to
learn how to reverse engineer and perform process injection into android and windows applications
hook functions and modify its behaviour
perform basic bypass of security restrictions on android and windows apps
Features of this course
Designed with beginners in mind.
Simple android apps and windows crackme's designed to learn process injection and function hooking
Practical and hands-on
Using free tools only
Suitable for
Reverse Engineering and Malware Analysis Students
Students planning on entering Malware Analysis and Reverse Engineering, or Penetration Testers as a Career Path
Security researchers
Prerequisite
Windows PC
Basic Java/jаvascript would be helpful but not mandatory
Preferably have an Android phone (non-rooted)
Enroll now and I will see you inside!
Who this course is for
Reverse engineering and malware analysis students
Security researchers
Penetration testers
https://fikper.com/hn82ihF7Vz/Udemy_Reverse_Engineering_Frida_for_Beginners.part1.rar.html
https://fikper.com/c5AwKZQvE3/Udemy_Reverse_Engineering_Frida_for_Beginners.part2.rar.html
https://rapidgator.net/file/734f43ebd0dc6151ef68770b9a3ab2f4/Udemy_Reverse_Engineering_Frida_for_Beginners.part1.rar
https://rapidgator.net/file/158dc69c278dd4c08272b429dfad2cf0/Udemy_Reverse_Engineering_Frida_for_Beginners.part2.rar
https://filestore.me/540hmbgj4125/Udemy_Reverse_Engineering_Frida_for_Beginners.part1.rar
https://filestore.me/8c6varclxre0/Udemy_Reverse_Engineering_Frida_for_Beginners.part2.rar
What you'll learn
Listing process libraries
Reversing Android apps
Hooking Classes and Functions
Examining and modifying function parameters and return values
Reversing windows app
Hooking process functions
Memory scanning
Process injection
Hacking memory
Decompiling apps
Bypassing root detection
Interceptinghttp andhttps traffic
Bypassing basic security mechanism for android and windows apps
Enumerating libraries and imported functions
and more..
Requirements
PC Laptop and non-rooted android phone (optional)
Basic Java/jаvascript would be helpful but not mandatory
Description
Frida is a dynamic instrumentation toolkit for developers, reverse-engineers, and security researchers. It allows you to inject your own scripts into black box processes. Hook any function, spy on crypto APIs or trace private application code, no source code needed. Edit, hit save, and instantly see the results. All without compilation steps or program restarts. It's the swiss army knife for process injections for native apps and is a popular dynamic code instrumentation toolkit. It lets you inject snippets of jаvascript or your own library into native apps on Windows and Android. It is the go-to tool you use for API tracing.
At the end of this course you will be able to
learn how to reverse engineer and perform process injection into android and windows applications
hook functions and modify its behaviour
perform basic bypass of security restrictions on android and windows apps
Features of this course
Designed with beginners in mind.
Simple android apps and windows crackme's designed to learn process injection and function hooking
Practical and hands-on
Using free tools only
Suitable for
Reverse Engineering and Malware Analysis Students
Students planning on entering Malware Analysis and Reverse Engineering, or Penetration Testers as a Career Path
Security researchers
Prerequisite
Windows PC
Basic Java/jаvascript would be helpful but not mandatory
Preferably have an Android phone (non-rooted)
Enroll now and I will see you inside!
Who this course is for
Reverse engineering and malware analysis students
Security researchers
Penetration testers
https://fikper.com/hn82ihF7Vz/Udemy_Reverse_Engineering_Frida_for_Beginners.part1.rar.html
https://fikper.com/c5AwKZQvE3/Udemy_Reverse_Engineering_Frida_for_Beginners.part2.rar.html
https://rapidgator.net/file/734f43ebd0dc6151ef68770b9a3ab2f4/Udemy_Reverse_Engineering_Frida_for_Beginners.part1.rar
https://rapidgator.net/file/158dc69c278dd4c08272b429dfad2cf0/Udemy_Reverse_Engineering_Frida_for_Beginners.part2.rar
https://filestore.me/540hmbgj4125/Udemy_Reverse_Engineering_Frida_for_Beginners.part1.rar
https://filestore.me/8c6varclxre0/Udemy_Reverse_Engineering_Frida_for_Beginners.part2.rar
We need your support!
Make a donation to help us stay online

Bitcoin (BTC)
bc1q08g9d22cxkawsjlf8etuek2pc9n2a3hs4cdrld

Bitcoin Cash (BCH)
qqvwexzhvgauxq2apgc4j0ewvcak6hh6lsnzmvtkem

Ethereum (ETH)
0xb55513D2c91A6e3c497621644ec99e206CDaf239

Litecoin (LTC)
ltc1qt6g2trfv9tjs4qj68sqc4uf0ukvc9jpnsyt59u

USDT (ERC20)
0xb55513D2c91A6e3c497621644ec99e206CDaf239

USDT (TRC20)
TYdPNrz7v1P9riWBWZ317oBgJueheGjATm
Information |
|||
 |
Users of GUESTS are not allowed to comment this publication. | ||