


Sniffing and Spoofing with Kali Linux
Category: Tutorials
- views: 176
- date: 15 April 2024
- posted by: AD-TEAM
Sniffing and Spoofing with Kali Linux
.MP4, AVC, 1280x720, 30 fps | English, AAC, 2 Ch | 48m | 111 MB
Instructor: Alexander Tushinsky
Having access to an internal network can provide a wealth of information, if you know how to look for it. This course will teach you Sniffing and Spoofing techniques using Ettercap and TCPDump.
What you'll learn
Once a foothold is established within a network, the next logical step is to try and capture the traffic of other systems to help gather intelligence. Having access to an internal network can provide a wealth of information, if you know how to look for it.
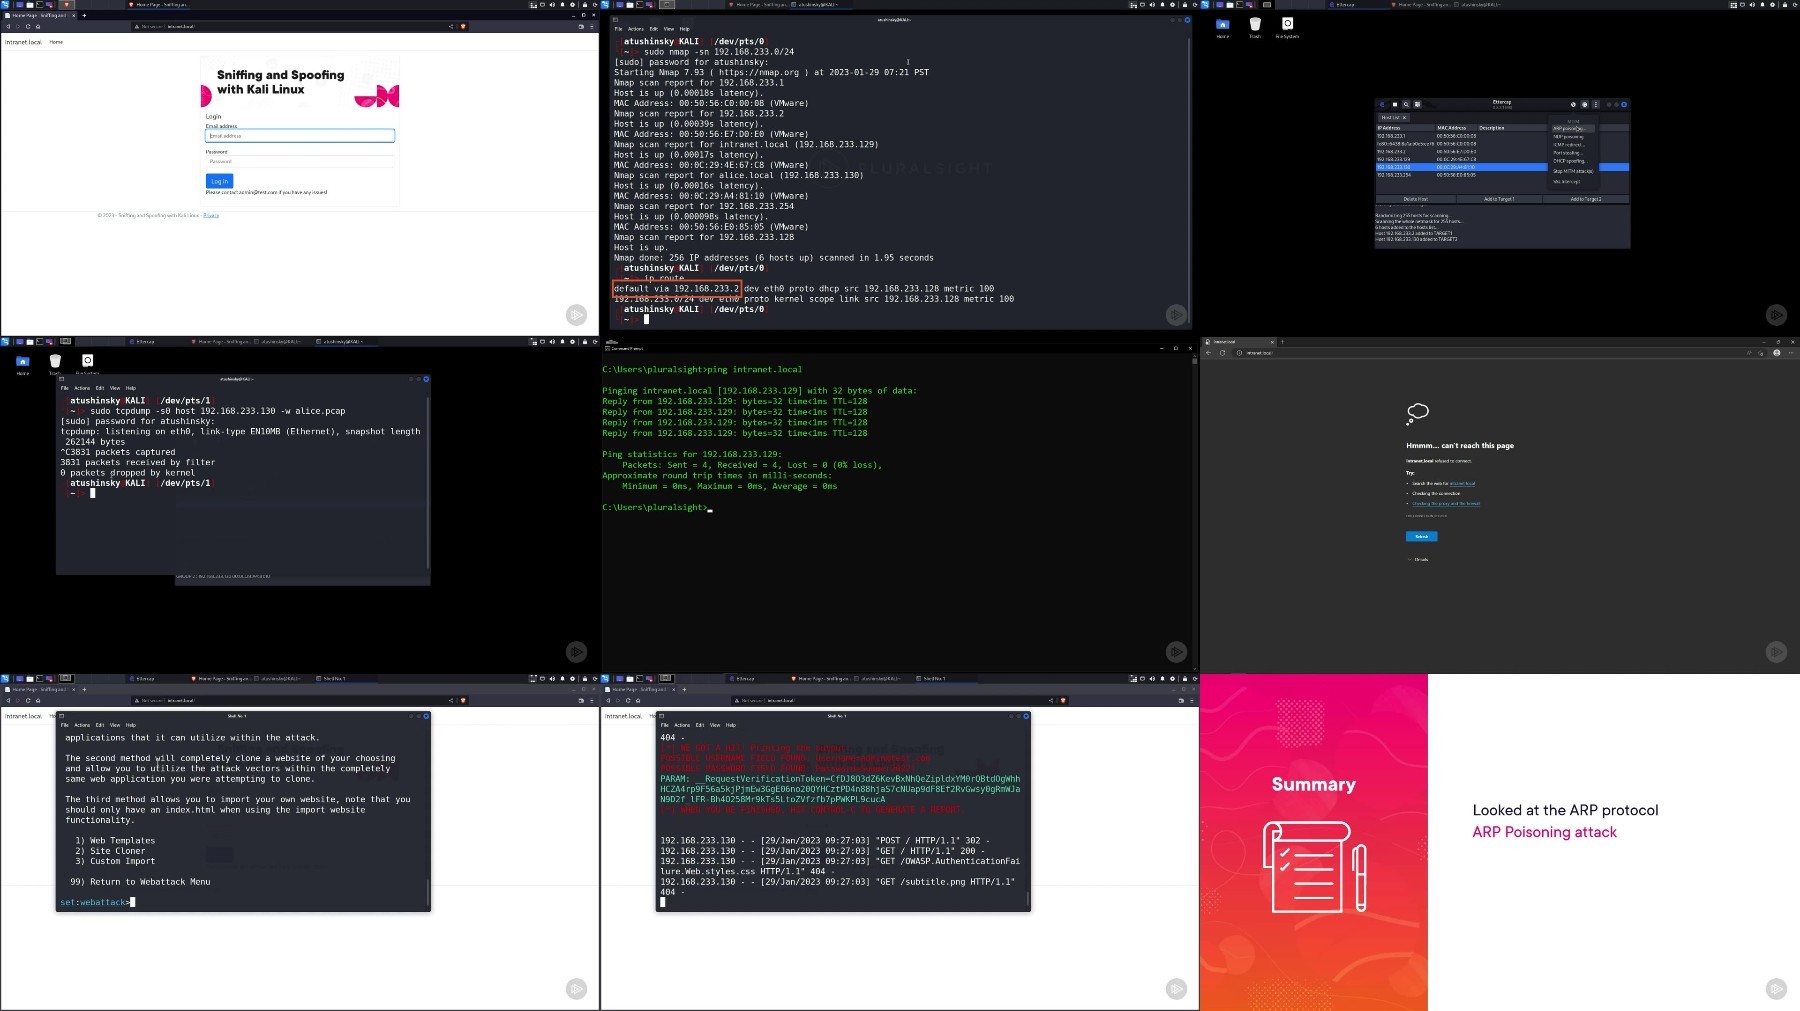
In this course, Sniffing and Spoofing with Kali Linux, you'll learn to use network packet inspection to your advantage. First, you'll explore the ability to sniff and look at network traffic by using Ettercap and TCPDump to create a MAC flood attack. Next, you'll discover how to perform an ARP poisoning attack, which establishes you as the "man-in-the-middle", spying on traffic between a target PC and the router. Finally, you can implement a DNS spoofing attack, which ultimately can easily help you establish an additional foothold and provide you with a great deal of information about our target. When you're finished with this course, you'll have the skills and knowledge to work with Ettercap and TCPDump, tools needed to perform sniffing and spoofing attacks as part of a penetration test.
More Info
Free search engine download: Pluralsight - Sniffing and Spoofing with Kali Linux 2023-2
We need your support!
Make a donation to help us stay online

Bitcoin (BTC)
bc1q08g9d22cxkawsjlf8etuek2pc9n2a3hs4cdrld

Bitcoin Cash (BCH)
qqvwexzhvgauxq2apgc4j0ewvcak6hh6lsnzmvtkem

Ethereum (ETH)
0xb55513D2c91A6e3c497621644ec99e206CDaf239

Litecoin (LTC)
ltc1qt6g2trfv9tjs4qj68sqc4uf0ukvc9jpnsyt59u

USDT (ERC20)
0xb55513D2c91A6e3c497621644ec99e206CDaf239

USDT (TRC20)
TYdPNrz7v1P9riWBWZ317oBgJueheGjATm
Information |
|||
 |
Users of GUESTS are not allowed to comment this publication. | ||